Closing the Remediation Loop: 8 Agentic PenTest AI Tools With Built-In Fix Validation
Traditional penetration testing has a well-known blind spot: a human team submits a report, engineers apply patches, and then weeks or months pass before anyone verifies whether the vulnerability is truly gone. Agentic AI pentesting platforms change that workflow. These tools deploy autonomous security agents that plan attacks, chain vulnerabilities, generate reproducible proof-of-concept exploits, and crucially — automatically replay those exact exploit paths once remediation is deployed.
For this roundup, we filtered only agentic platforms that support targeted retesting after fixes, not just scheduled periodic scans. Each entry was evaluated on attack chaining capability, retest reliability, false-positive control, integration with issue trackers, scope guardrails, and evidence quality.
1. Strobes
Strobes is built around end-to-end continuous threat exposure management (CTEM), with multi-agent orchestration covering apps, APIs, cloud infrastructure and identity surfaces. Once an agent validates an exploit, the finding syncs directly to Jira, GitHub or Azure DevOps with full PoC traces and reproduction steps. When engineers mark the ticket as resolved, Strobes’ dedicated validation agents automatically replay the attack chain to confirm closure, rather than relying on manual status updates.
Pros
- Automatic retest trigger tied to remediation ticket state
- Agents retain environment memory across testing cycles
- Strong attack-path chaining for lateral movement and privilege escalation
- Configurable human approval for high-risk exploit actions
Cons
- Enterprise-focused pricing, overkill for small teams
- Setup requires mapping your entire asset inventory
- Retest workflows are most powerful when paired with their native ticketing
Best for: SecOps teams that need continuous validation across hybrid cloud and on-prem assets.
2. Aikido Infinite
Aikido Infinite targets web app and API security, designed to run focused retests on every deployment. Its RunSybil agent replays previously successful exploit sequences against new builds, isolating testing only to code changes rather than rerunning a full pentest every time. It also ships AutoFix functionality, which generates pull requests for confirmed bugs and then validates the patch by re-running the original exploit payload.
Pros
- CI/CD-native retesting on every pull request and deploy
- Lightweight, change-scoped retests for fast feedback
- Supports self-hosted inference with Aikido Machine for regulated environments
- One-click manual retest for ad-hoc validation
Cons
- Coverage is focused on applications and APIs, less strong for internal network red teaming
- Deep exploitation requires source-code integration
- Some advanced retest rules sit behind enterprise tiers
Best for: AppSec and engineering teams shifting security validation left into the development pipeline.
3. NodeZero (Horizon3.ai)
NodeZero is one of the most established autonomous pentesting platforms for internal networks, Active Directory, identity systems and cloud environments. Its agents chain misconfigurations, credential flaws and access gaps to build real compromise paths. After remediation, it runs targeted validation campaigns to confirm the attack chain is broken, not just a single isolated check fixed.
Pros
- Excellent at identity and Active Directory attack-path validation
- Safe, non-destructive exploitation by design
- Retest campaigns can be scheduled or triggered manually from findings
- Auditor-ready evidence and attack graphs
Cons
- Not optimized for deep web application business-logic testing
- Can take time to learn the layout of complex segmented networks
- Higher minimum scope for internal deployments
Best for: Internal red team validation, Active Directory hygiene, and identity risk remediation checks.
4. Novee
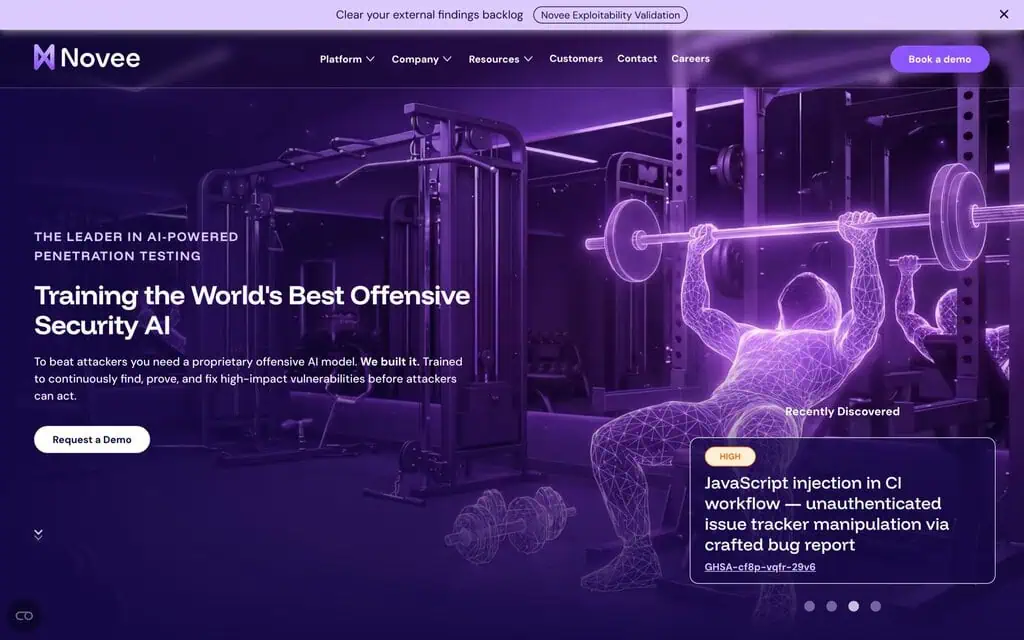
Novee is an autonomous red-teaming platform that deploys hive-style AI agents to map attack surfaces and validate high-impact exploit chains across cloud, identity and application layers. Every validated finding stores its full attack sequence, which the platform replays automatically once a fix is deployed. It prioritizes validated risk over raw vulnerability count, helping teams avoid wasting cycles on theoretical CVEs.
Pros
- True black-box testing; only requires a root domain to start
- Non-destructive payloads to avoid production disruption
- Continuous attack-surface drift detection between retests
- Automatic retest alerts sent directly to security channels
Cons
- Complex attack chains sometimes require human follow-up analysis
- Limited deep API fuzzing compared to dedicated AppSec tools
- Newer platform with a smaller ecosystem of integrations
Best for: Cloud-native enterprises wanting autonomous red-team validation without full-time red team staffing.
5. Pensar
Pensar is built around a tight patch-retest loop for developer-first security. Its offensive agents exploit a target, generate a patch PR, then immediately re-run the exploit variant analysis to confirm the patch blocks all permutations of the original attack — not just the exact payload captured in the initial PoC. This helps catch incomplete fixes that leave alternate exploit vectors open.
Pros
- Variant retesting, not just simple replay of one payload
- Native CLI and GitHub Action integration
- Built for developer workflows, not just SecOps dashboards
- Lightweight for staging and pre-production environments
Cons
- Focused heavily on web apps and custom code, not broad infrastructure
- Less suited for large-scale network pentest campaigns
- Requires staging environments that mirror production
Best for: Developer security teams that want proof patches block all related exploit variants.
6. Strix
Strix is an open-source agentic pentesting agent that runs via CLI, designed to test web apps and APIs during development. After it successfully exploits a flaw and submits a suggested patch, it automatically replays its own exploit sequence against the patched endpoint. It works inside GitHub Actions and supports bring-your-own LLM keys, giving teams full control of the agent logic and retest rules.
Pros
- Open-source core, fully auditable agent behavior
- Zero vendor lock-in for retest workflows
- Great for custom internal security pipelines
- Low cost for small teams
Cons
- Steeper setup and prompt engineering overhead
- No managed SaaS dashboard by default
- Retest logic must be configured carefully to avoid noisy false negatives
Best for: Security engineers who want self-hosted, customizable agentic testing inside their CI pipeline.
7. Corgea
Corgea uses a multi-agent architecture with specialist sub-agents for authentication discovery, API exploration, injection testing and business logic auditing. After a vulnerability is confirmed, its coordinator agent orchestrates a focused retest campaign that mimics the original attacker workflow, verifying that the entire path is blocked rather than a single parameter patched. It supports both on-demand and continuous autonomous pentest cycles.
Pros
- Code-aware reasoning for business logic flaws
- Granular retest scope control
- Detailed attack narrative reports for auditors
- Human-in-the-loop approval for high-impact exploitation
Cons
- Newer platform, fewer third-party integrations
- Retest speed slows on extremely large monolithic applications
- Pricing information is mostly custom enterprise quotes
Best for: Teams testing complex custom web apps with heavy business logic risk.
8. Scanifier
Scanifier is an autonomous offensive AI pentesting tool built for speed and simple validation. After generating a reproducible PoC for a confirmed vulnerability, it offers a free automated retest to confirm remediation before closing the finding. It keeps retests lightweight and focused, avoiding full re-pentests unless you explicitly schedule them, making it a strong fit for teams that want fast proof without heavy operational overhead.
Pros
- Fast setup; start testing from a domain in under a minute
- Free targeted retests for validated findings
- Simple dashboard with clear PoC evidence
- Production-safe execution controls
Cons
- Less deep attack-chaining capability than NodeZero or Novee
- Fewer advanced identity and AD test modules
- Best for external surfaces, not internal network red teaming
Best for: Mid-sized teams that need straightforward external pentesting and quick remediation validation.
Our Evaluation Framework for Retest-Capable Agentic Pentest Tools
We only included platforms that meet all three core criteria:
- Agentic reasoning: Not static scanners; agents adapt their attack path based on target responses
- Stored exploit context: They preserve the exact sequence of requests/payloads used to validate the flaw
- Targeted retesting: Can replay the validated exploit after a fix, separate from a full new pentest
Secondary factors we weighed: CI/CD integration, ticket-system triggers, variant testing, safety guardrails, audit trails, and whether retest results distinguish between “patch blocked the exploit” and “the target changed for unrelated reasons.”
Key Risks to Understand
Automated retesting is powerful, but it has limits. Agents can only replay the exploit paths they discovered initially; they will not automatically find brand-new bypasses or secondary flaws introduced by your patch. For critical systems, combine agentic retests with periodic manual pentest reviews. Always set strict scope rules, authorization and safety controls before running autonomous exploitation agents against production.
Final Recommendation Cheat Sheet
✅ CI/CD appsec + deploy-time retests: Aikido Infinite ✅ Internal network / Active Directory validation: NodeZero ✅ Developer patch + variant retesting: Pensar ✅ Open-source self-hosted pipelines: Strix ✅ Enterprise cloud red-team continuous validation: Novee or Strobes
Agentic pentesting is not replacing human pentesters, but these eight tools eliminate the most tedious part of the vulnerability lifecycle: manually proving whether your fixes actually work.